
KMS Performance Comparison
Versions: v5.28.0
Generated: 2026-10-09
Benchmark Environment
| Field | Value |
|---|---|
| Date | 2026-10-07 22:25:18 UTC |
| HSM backend | SoftHSM2 |
| Command | mise run bench:pkcs11 --delegated --hsm-model softhsm2 |
| Build | bench / non-fips |
| Database | SQLite (temporary, single benchmark run) |
| CPU | Intel(R) Core(TM) i9-14900T @ 857 MHz |
| CPU cores | 24 physical / 32 logical (HT) |
| RAM | 31.1 GB |
| OS | Ubuntu 24.04.5 LTS |
| Kernel | 6.8.0-146-generic |
Load test parameters
| Parameter | Value |
|---|---|
| Mode | all |
| Protocols | pkcs11 |
| Measurement window | 20 s per concurrency level |
| Concurrency levels | 1,2,4,8,16 |
| Warm-up | 5 s |
| Cooldown between levels | 2 s |
CPU detail (lscpu)
Architecture:                            x86_64
CPU op-mode(s):                          32-bit, 64-bit
Address sizes:                           46 bits physical, 48 bits virtual
Byte Order:                              Little Endian
CPU(s):                                  32
On-line CPU(s) list:                     0-31
Vendor ID:                               GenuineIntel
Model name:                              Intel(R) Core(TM) i9-14900T
CPU family:                              6
Model:                                   183
Thread(s) per core:                      2
Core(s) per socket:                      24
Socket(s):                               1
Stepping:                                1
CPU(s) scaling MHz:                      22%
CPU max MHz:                             5500,0000
CPU min MHz:                             800,0000
BogoMIPS:                                2227,20
Flags:                                   fpu vme de pse tsc msr pae mce cx8 apic sep mtrr pge mca cmov pat pse36 clflush dts acpi mmx fxsr sse sse2 ss ht tm pbe syscall nx pdpe1gb rdtscp lm constant_tsc art arch_perfmon pebs bts rep_good nopl xtopology nonstop_tsc cpuid aperfmperf tsc_known_freq pni pclmulqdq dtes64 monitor ds_cpl vmx smx est tm2 ssse3 sdbg fma cx16 xtpr pdcm pcid sse4_1 sse4_2 x2apic movbe popcnt tsc_deadline_timer aes xsave avx f16c rdrand lahf_lm abm 3dnowprefetch cpuid_fault epb ssbd ibrs ibpb stibp ibrs_enhanced tpr_shadow flexpriority ept vpid ept_ad fsgsbase tsc_adjust bmi1 avx2 smep bmi2 erms invpcid rdseed adx smap clflushopt clwb intel_pt sha_ni xsaveopt xsavec xgetbv1 xsaves split_lock_detect user_shstk avx_vnni dtherm ida arat pln pts hwp hwp_notify hwp_act_window hwp_epp hwp_pkg_req hfi vnmi umip pku ospke waitpkg gfni vaes vpclmulqdq tme rdpid movdiri movdir64b fsrm md_clear serialize pconfig arch_lbr ibt flush_l1d arch_capabilities ibpb_exit_to_user
Virtualization:                          VT-x
L1d cache:                               896 KiB (24 instances)
L1i cache:                               1,3 MiB (24 instances)
L2 cache:                                32 MiB (12 instances)
L3 cache:                                36 MiB (1 instance)
NUMA node(s):                            1
NUMA node0 CPU(s):                       0-31
Vulnerability Gather data sampling:      Not affected
Vulnerability Indirect target selection: Not affected
Vulnerability Itlb multihit:             Not affected
Vulnerability L1tf:                      Not affected
Vulnerability Mds:                       Not affected
Vulnerability Meltdown:                  Not affected
Vulnerability Mmio stale data:           Not affected
Vulnerability Reg file data sampling:    Mitigation; Clear Register File
Vulnerability Retbleed:                  Not affected
Vulnerability Spec rstack overflow:      Not affected
Vulnerability Spec store bypass:         Mitigation; Speculative Store Bypass disabled via prctl
Vulnerability Spectre v1:                Mitigation; usercopy/swapgs barriers and __user pointer sanitization
Vulnerability Spectre v2:                Mitigation; Enhanced / Automatic IBRS; IBPB conditional; PBRSB-eIBRS SW sequence; BHI BHI_DIS_S
Vulnerability Srbds:                     Not affected
Vulnerability Tsa:                       Not affected
Vulnerability Tsx async abort:           Not affected
Vulnerability Vmscape:                   Mitigation; IBPB before exit to userspace
Architecture
graph TB
    subgraph cli["Local Machine"]
        ckms["<b>ckms pkcs11 bench</b>"]
        lib["<b>cosmian_pkcs11.so</b>"]
    end

    subgraph srv["KMS Server"]
        kmip["KMIP 2.1"]
        oracle["CryptoOracle"]
    end

    subgraph hsm["SoftHSM2"]
        slot["PKCS#11 Slot"]
        keys["ECDSA<br/>RSA<br/>EdDSA<br/>AES<br/>(Resident)"]
    end

    ckms -->|C_Sign/C_Verify/C_Encrypt/C_Decrypt/C_GenerateKey| lib
    lib -->|HTTP| kmip
    kmip --> oracle
    oracle -->|PKCS#11| slot
    slot --> keys

    style ckms fill:#4A90E2
    style lib fill:#FF6B6B
    style kmip fill:#7ED321
    style oracle fill:#F5A623
    style slot fill:#BD10E0
Components:
- ckms: PKCS#11 load test driver (
mise run bench:pkcs11 --delegated --hsm-model softhsm2) - cosmian_pkcs11.so: PKCS#11 provider bridge
- KMIP Endpoint: Server-side protocol handler
- CryptoOracle: Routes operations to HSM-resident keys (C_Sign/C_Verify/C_Encrypt/C_Decrypt/C_GenerateKey on SoftHSM2)
- PKCS#11 Slot: SoftHSM2 backend for key storage and cryptographic ops
Protocols
The caller-facing protocol benchmarked here is the cosmian_pkcs11 provider's real PKCS#11 v3.1 Cryptoki C ABI: the benchmark dlopen()s the built shared library (libcosmian_pkcs11.{so,dylib}) and resolves its standard interface through C_GetInterface — the same call path v3-aware PKCS#11 consumers (Oracle TDE, OpenSSH, disk-encryption tools) use. For remote Sign, the provider wraps the KMIP operation in a KMIP 2.1 RequestMessage, serializes binary TTLV, and sends application/octet-stream to POST /kmip; the binary TTLV response is fully deserialized before C_SignMessage returns.
This delegated variant provisions hsm::<slot>::... keys. After the provider sends each KMIP request, KMS routes the key to its CryptoOracle; the cryptographic operation executes through the server-side SoftHSM2 PKCS#11 backend rather than software crypto.
| Interface | Transport | Description |
|---|---|---|
| PKCS#11 (Cryptoki v3.1) | C_GetInterface + C ABI | C_Initialize, C_OpenSession, C_EncryptInit/C_Encrypt, C_DecryptInit/C_Decrypt, C_MessageSignInit/C_SignMessage, C_VerifyInit/C_Verify, C_GenerateKey |
| Provider → KMS Sign | KMIP 2.1 binary TTLV over HTTP | POST /kmip, application/octet-stream |
| KMS → HSM | PKCS#11 via CryptoOracle | HSM-resident key generation and cryptographic operations |
Benchmark Methodology
Real Cryptoki C ABI, one session per worker
The benchmark subcommand ckms pkcs11 bench (driven by mise run bench:pkcs11 --delegated --hsm-model softhsm2) dlopen()s the built cosmian_pkcs11 shared library, resolves the v3.1 function table through C_GetInterface, and calls it directly — the same code path a real PKCS#11 consumer application uses, as opposed to mise bench:load, which drives the KMIP REST API directly through the ckms client library.
By default each worker thread owns a dedicated C_OpenSession handle. The provider looks the handle up in its session map and serializes only access to that individual session with a per-session lock, so unrelated worker sessions can progress independently. --shared-session is an opt-in comparison mode that reproduces the former single-session contention model; it is not the default methodology.
For the Ed25519 Sign path measured in this report, C_MessageSignInit runs once during setup and each C_SignMessage crosses the synchronous PKCS#11 boundary, builds a KMIP 2.1 RequestMessage, serializes it as binary TTLV, sends it to the /kmip octet-stream endpoint, and parses the binary TTLV response before copying the signature into the caller-owned buffer.
HSM-resident key execution
With --delegated, provisioning assigns hsm::<slot>::... UIDs and persists discovery tags in a versioned PKCS#11 CKA_LABEL envelope while retaining the raw key ID in CKA_ID. The provider locates those tagged keys through KMS, while operations are executed by the KMS CryptoOracle on the SoftHSM2 backend. For full test suites on simulator tokens, submodes run against separate fresh tokens so cumulative key generation does not contaminate later measurements.
Independent operations
Unlike the software/HSM reports where requests may be bundled, this report measures each Cryptoki operation independently:
- Encryption/Decryption:
C_EncryptInit/C_EncryptandC_DecryptInit/C_Decryptagainst pre-generated ciphertext - Sign:
C_SignInit/C_Sign(orC_MessageSignInit/C_SignMessagefor Ed25519) crossing the synchronous PKCS#11 boundary - Verify:
C_VerifyInit/C_Verifyimplemented and benchmarked through the real Cryptoki function table - Key Creation: symmetric
C_GenerateKeywith immediateC_DestroyObjectper iteration
Load test (mise run bench:pkcs11 --delegated --hsm-model softhsm2)
The load test sweeps a configurable list of concurrency levels, mirroring mise bench:load's own sweep mechanics exactly: at each level N concurrent OS threads call the target Cryptoki function in a tight loop for a fixed measurement window (default: 20 s), preceded by a warm-up phase (default: 5 s) that is excluded from measurements, followed by a cooldown (default: 2 s) before the next level.
Recorded metrics per (operation, concurrency) pair:
- Throughput — Cryptoki calls per second
- p50 / p95 / p99 — per-call latency percentiles (ms)
Infrastructure note: The benchmark server uses a local SQLite backend (temporary, discarded after the run). Throughput figures will differ on a production deployment backed by PostgreSQL or Redis-Findex.
Load Tests
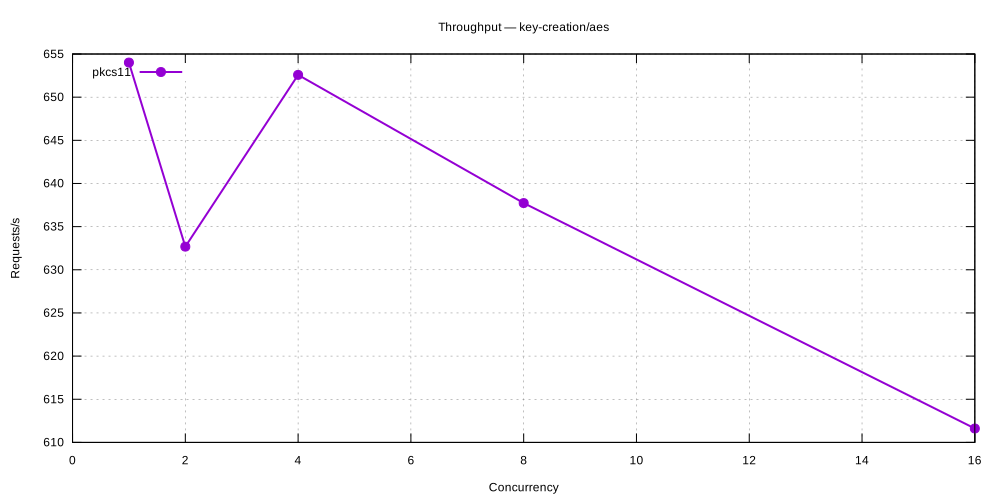
key-creation/aes
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 654 |
| 2 | 633 |
| 4 | 653 |
| 8 | 638 |
| 16 | 612 |
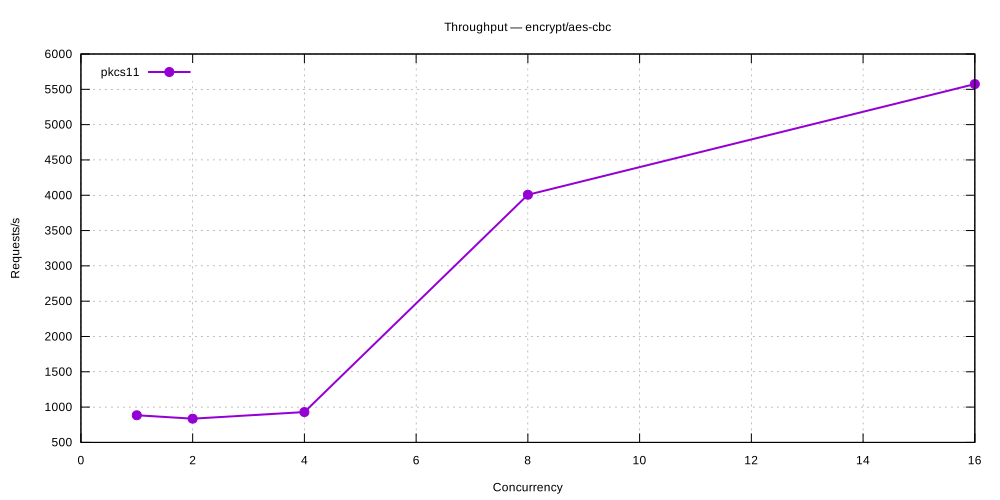
encrypt/aes-cbc
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 884 |
| 2 | 836 |
| 4 | 930 |
| 8 | 4,007 |
| 16 | 5,574 |
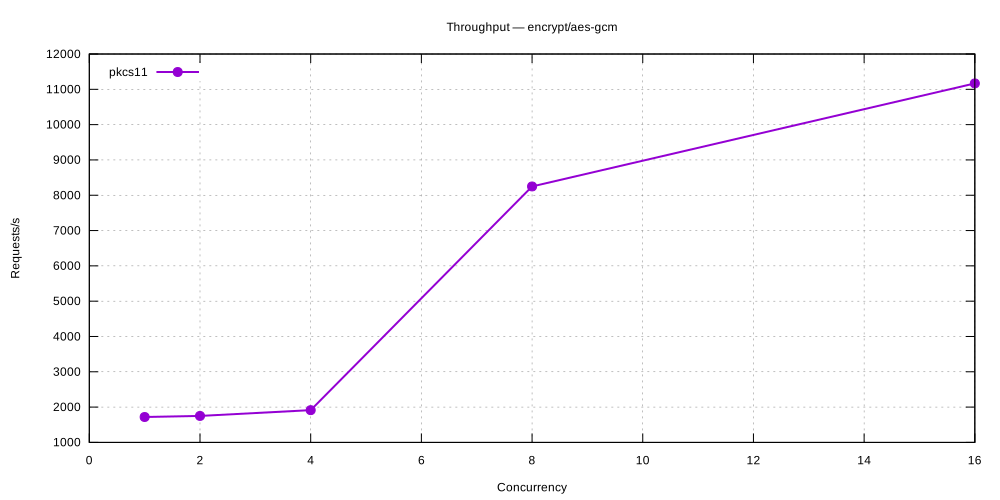
encrypt/aes-gcm
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,719 |
| 2 | 1,750 |
| 4 | 1,914 |
| 8 | 8,249 |
| 16 | 11,168 |
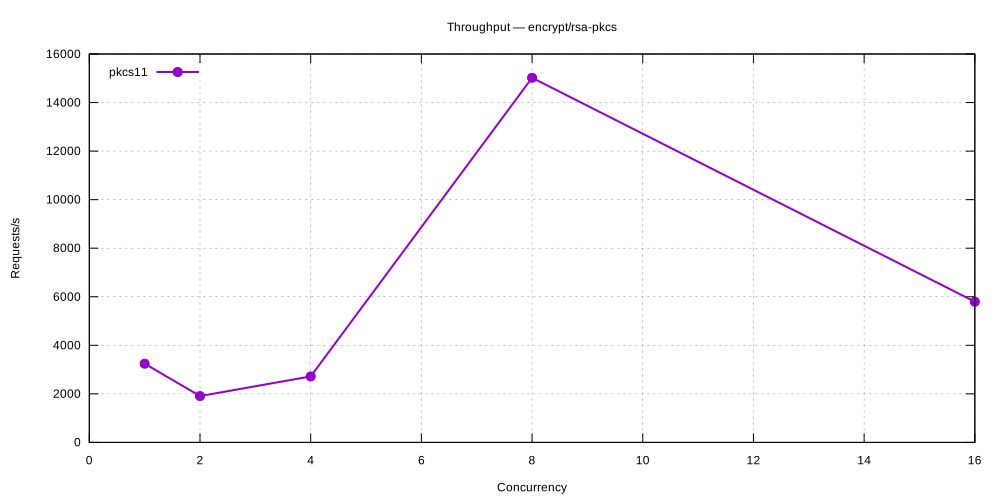
encrypt/rsa-pkcs
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 3,242 |
| 2 | 1,909 |
| 4 | 2,718 |
| 8 | 15,020 |
| 16 | 5,794 |
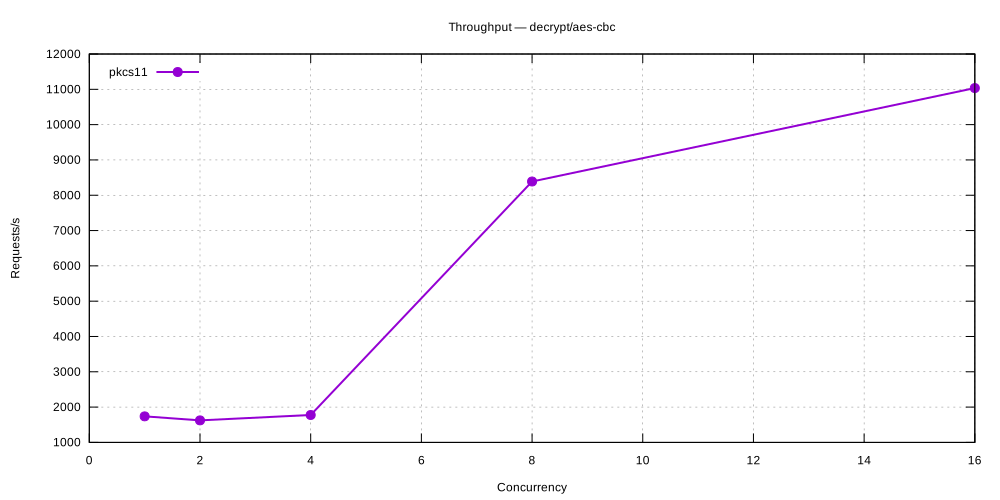
decrypt/aes-cbc
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,738 |
| 2 | 1,624 |
| 4 | 1,776 |
| 8 | 8,389 |
| 16 | 11,036 |
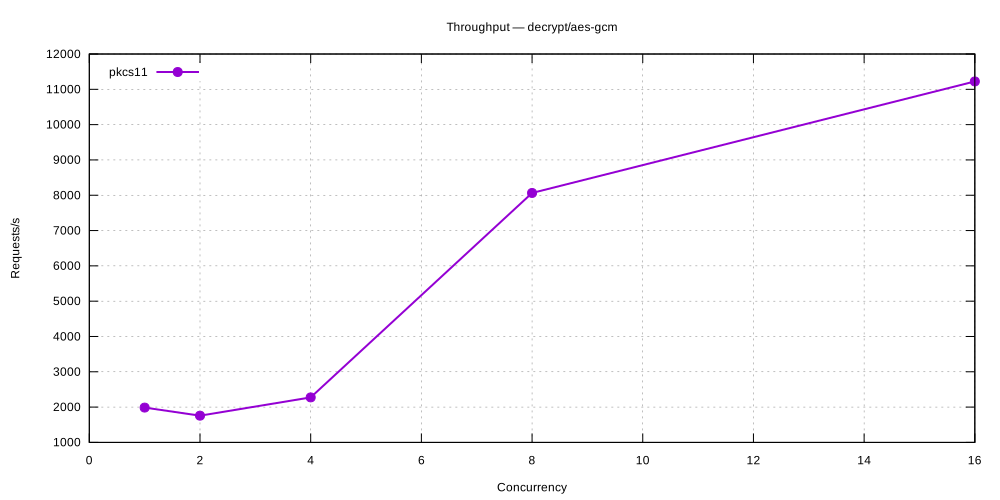
decrypt/aes-gcm
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,986 |
| 2 | 1,757 |
| 4 | 2,275 |
| 8 | 8,064 |
| 16 | 11,223 |
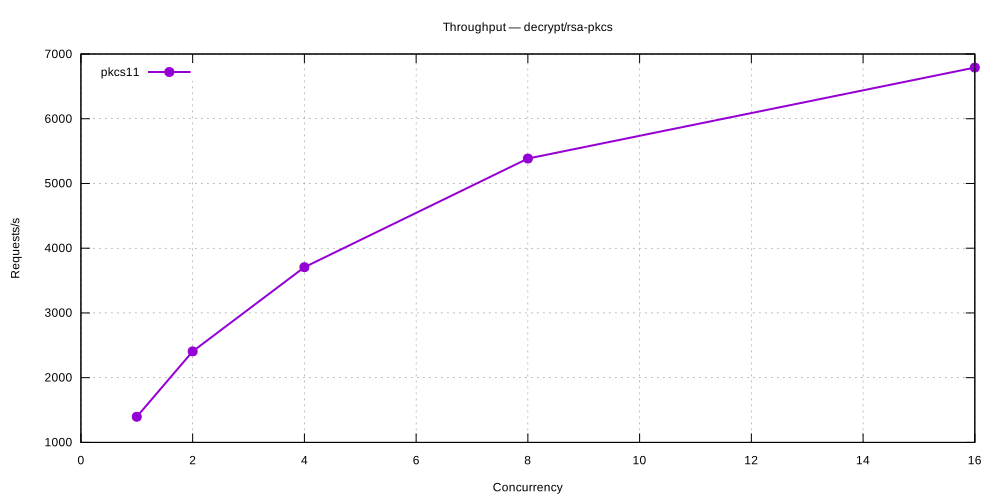
decrypt/rsa-pkcs
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,396 |
| 2 | 2,406 |
| 4 | 3,707 |
| 8 | 5,385 |
| 16 | 6,791 |
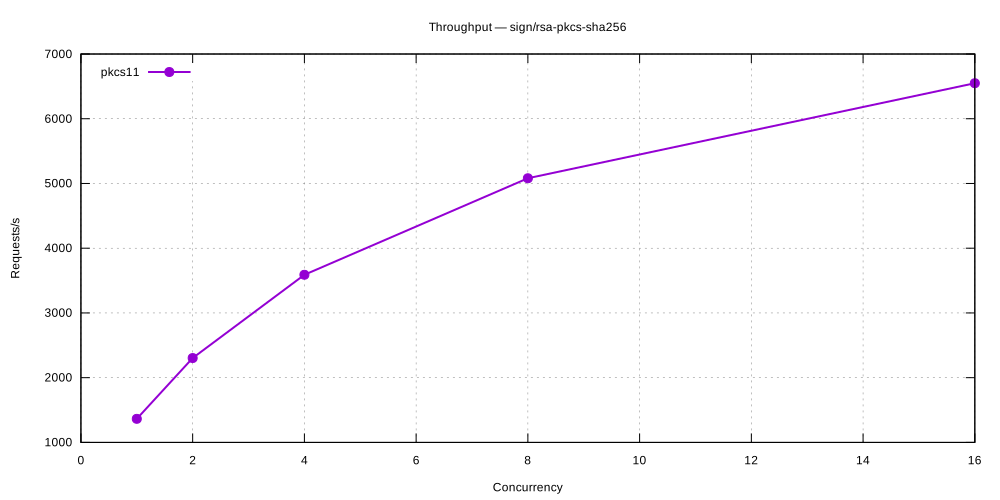
sign/rsa-pkcs-sha256
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,364 |
| 2 | 2,303 |
| 4 | 3,590 |
| 8 | 5,081 |
| 16 | 6,549 |
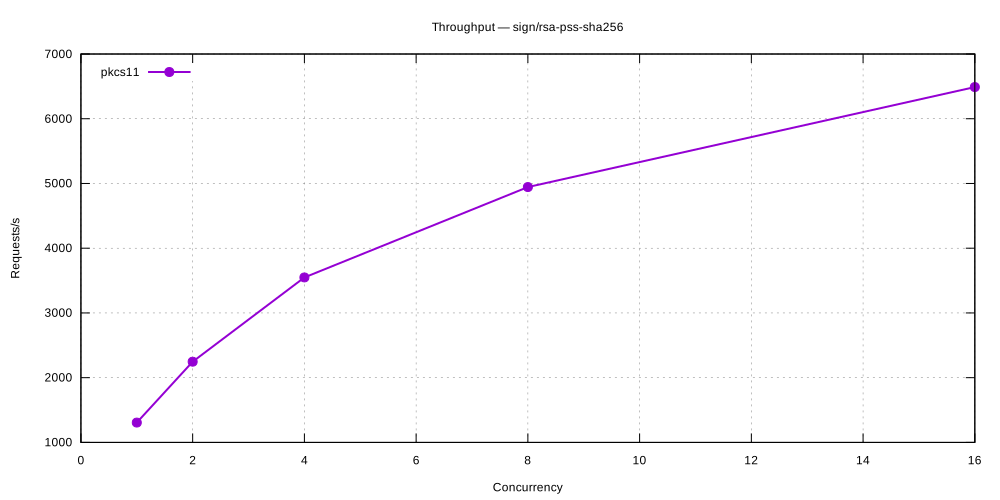
sign/rsa-pss-sha256
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,306 |
| 2 | 2,247 |
| 4 | 3,549 |
| 8 | 4,945 |
| 16 | 6,490 |
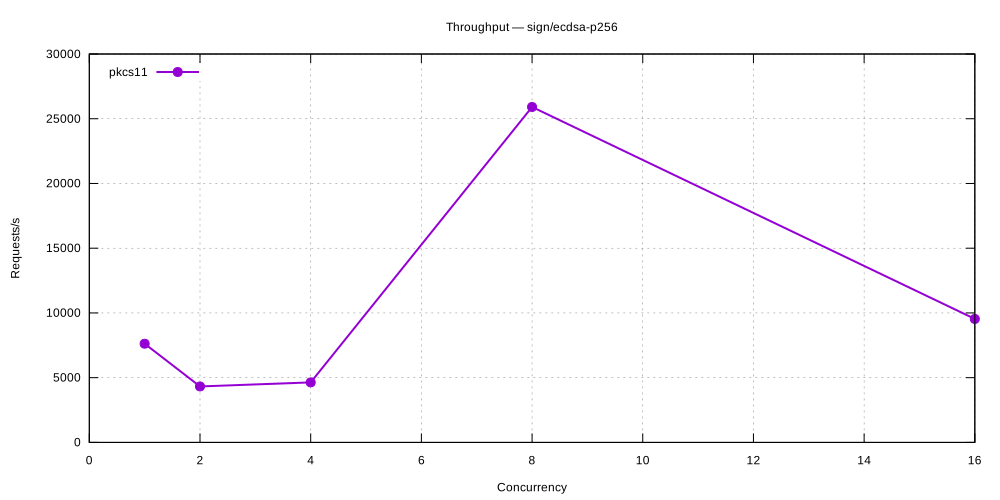
sign/ecdsa-p256
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 7,623 |
| 2 | 4,322 |
| 4 | 4,635 |
| 8 | 25,908 |
| 16 | 9,536 |
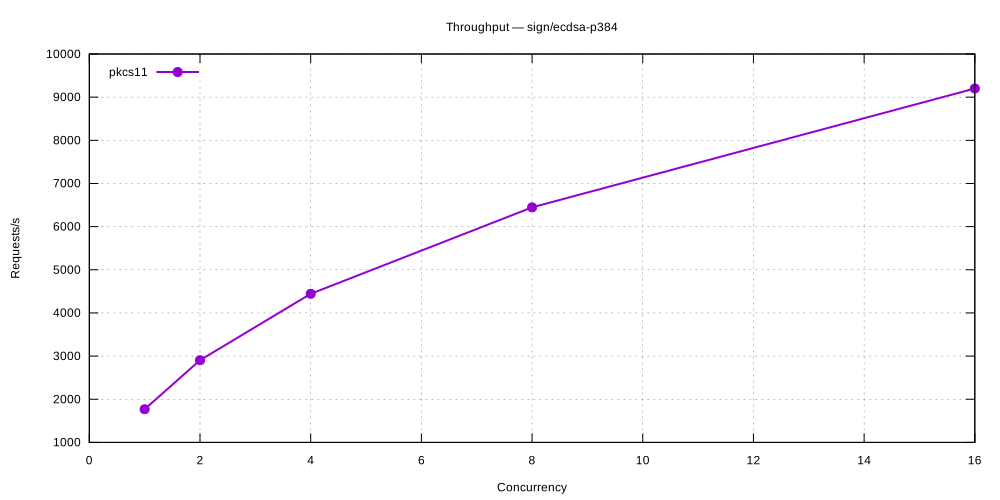
sign/ecdsa-p384
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,769 |
| 2 | 2,905 |
| 4 | 4,443 |
| 8 | 6,447 |
| 16 | 9,202 |
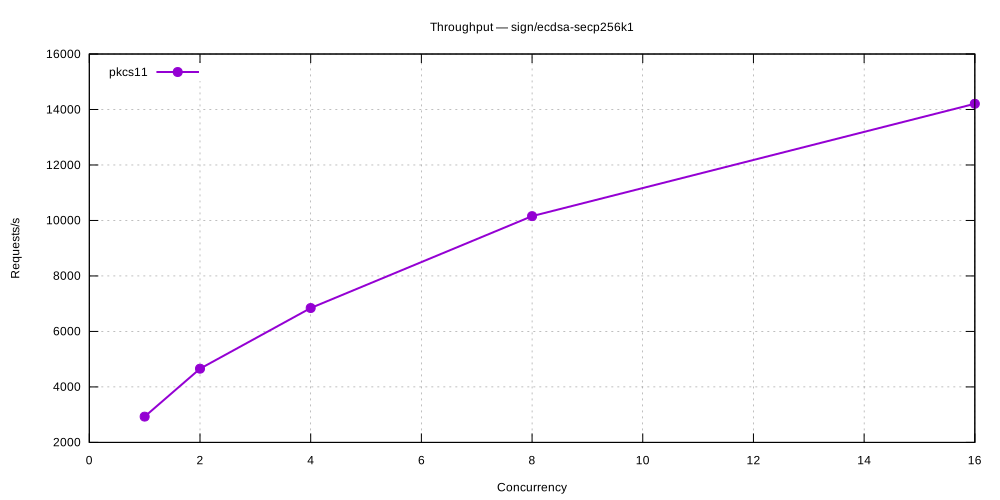
sign/ecdsa-secp256k1
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 2,929 |
| 2 | 4,657 |
| 4 | 6,844 |
| 8 | 10,156 |
| 16 | 14,206 |
sign/eddsa-ed25519
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 5,679 |
| 2 | 4,375 |
| 4 | 5,433 |
| 8 | 23,428 |
| 16 | 9,627 |
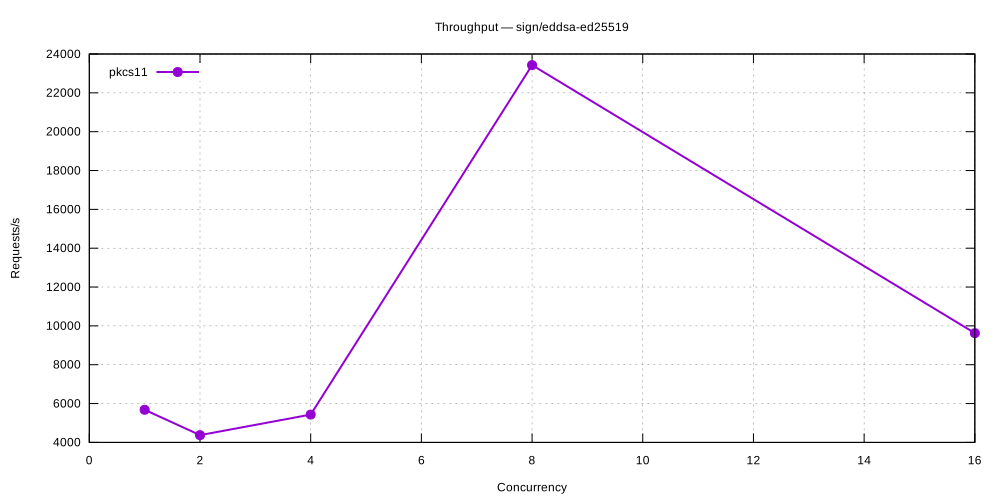
verify/rsa-pkcs-sha256
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 9,420 |
| 2 | 5,523 |
| 4 | 6,142 |
| 8 | 32,265 |
| 16 | 19,487 |
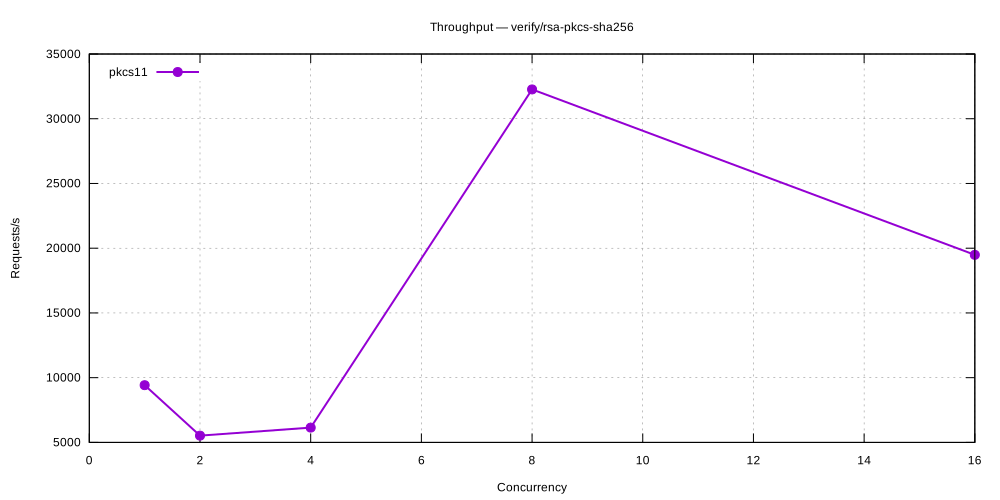
verify/rsa-pss-sha256
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 8,921 |
| 2 | 5,254 |
| 4 | 5,572 |
| 8 | 31,241 |
| 16 | 12,455 |
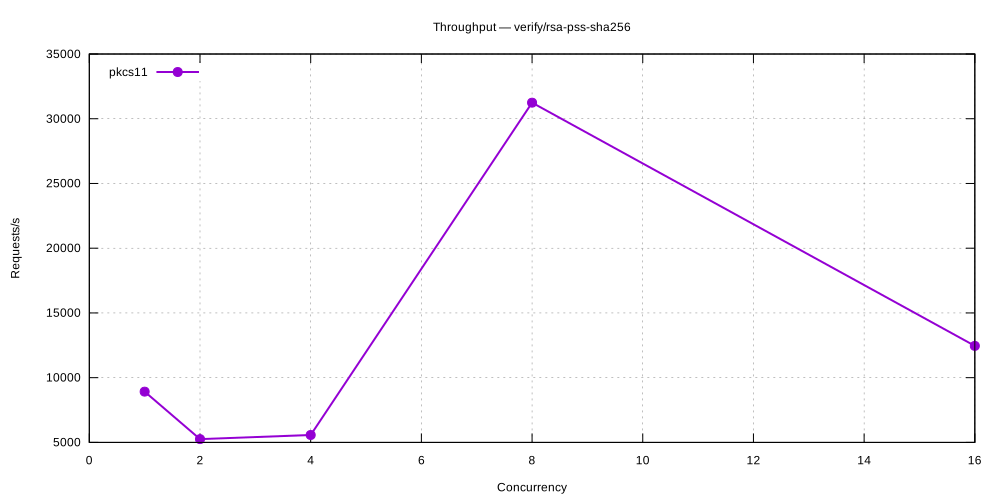
verify/ecdsa-p256
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 6,489 |
| 2 | 8,413 |
| 4 | 11,917 |
| 8 | 14,400 |
| 16 | 6,203 |
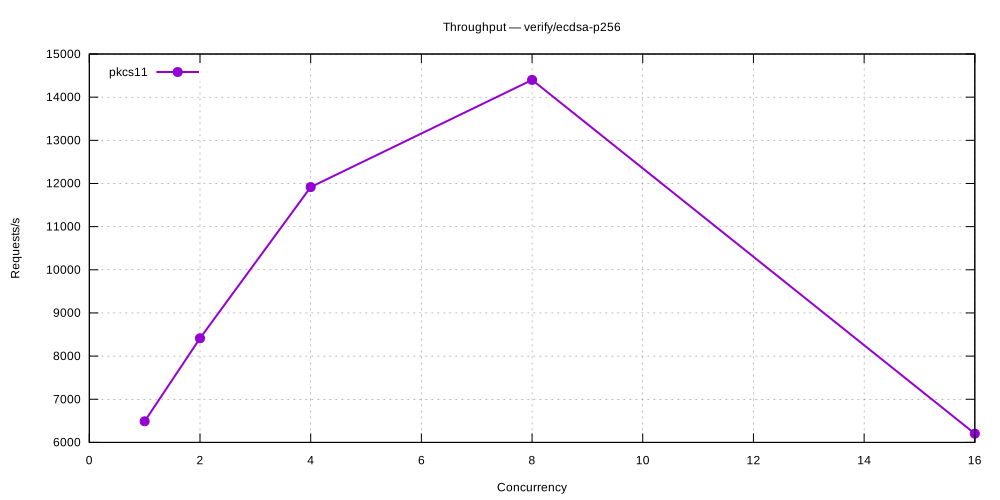
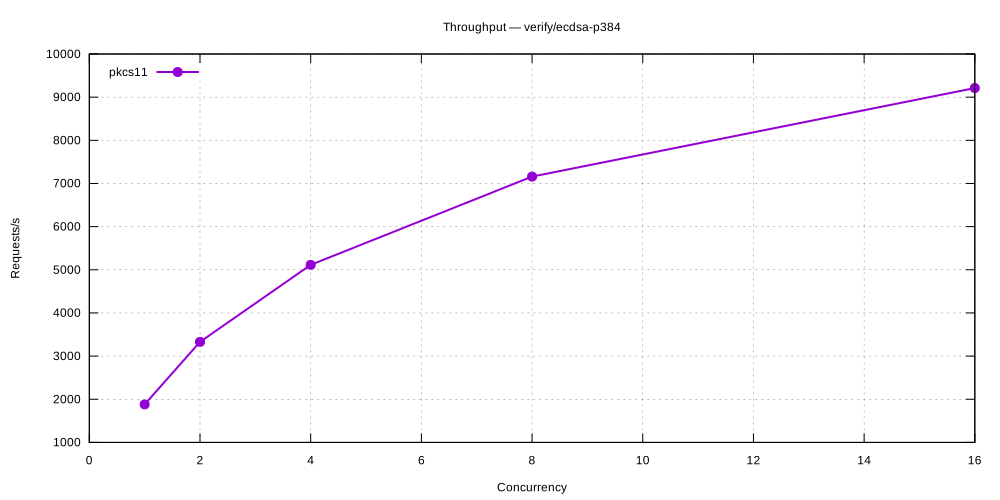
verify/ecdsa-p384
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 1,880 |
| 2 | 3,329 |
| 4 | 5,115 |
| 8 | 7,159 |
| 16 | 9,211 |
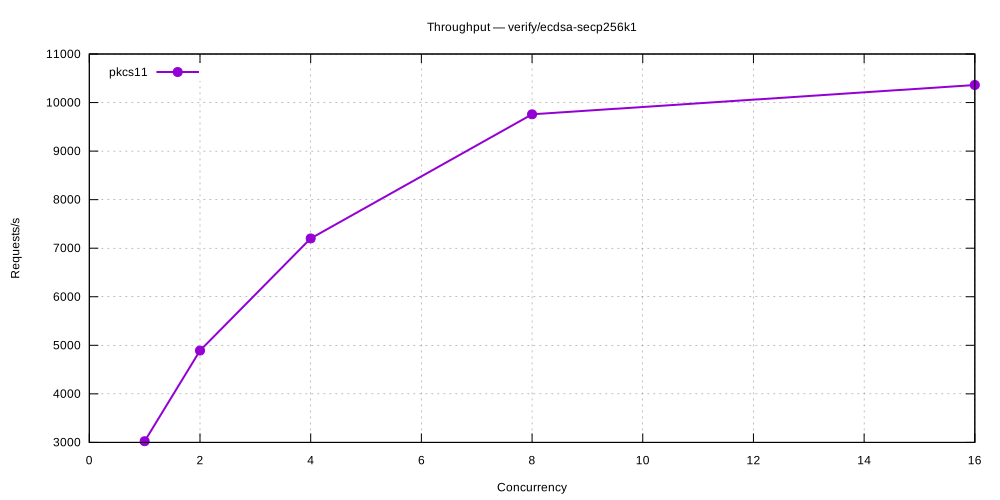
verify/ecdsa-secp256k1
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 3,024 |
| 2 | 4,892 |
| 4 | 7,201 |
| 8 | 9,758 |
| 16 | 10,362 |
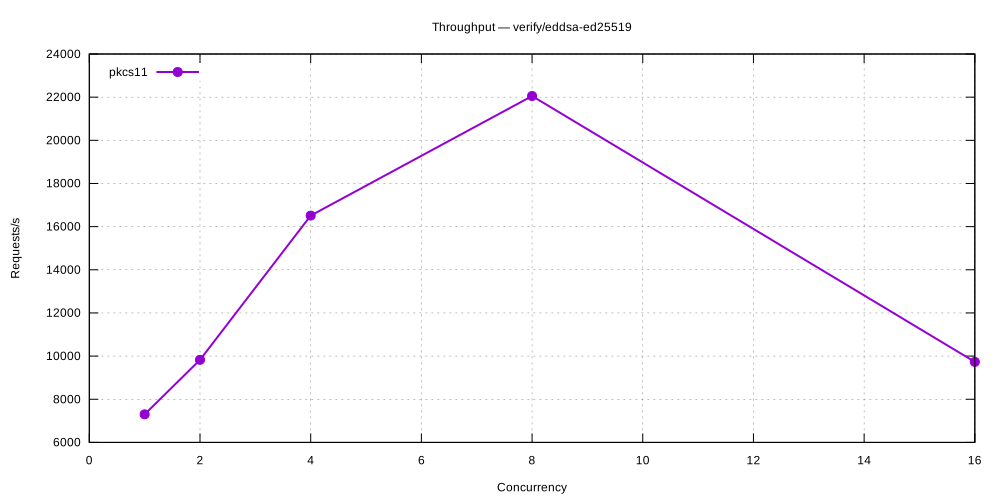
verify/eddsa-ed25519
| Concurrency | pkcs11 (req/s) |
|---|---|
| 1 | 7,302 |
| 2 | 9,826 |
| 4 | 16,512 |
| 8 | 22,053 |
| 16 | 9,731 |
Criterion Benchmarks
Symmetric Encryption
| Benchmark | pkcs11 |
|---|---|
| aes-cbc | 1.48 ms |
| aes-gcm | 498.8 µs |
Asymmetric Encryption
| Benchmark | pkcs11 |
|---|---|
| rsa-pkcs | 281.1 µs |
Sign / Verify
| Benchmark | pkcs11 |
|---|---|
| ecdsa-p256/sign | 159.8 µs |
| ecdsa-p256/verify | 206.4 µs |
| ecdsa-p384/sign | 905.1 µs |
| ecdsa-p384/verify | 621.7 µs |
| ecdsa-secp256k1/sign | 328.3 µs |
| ecdsa-secp256k1/verify | 320.6 µs |
| eddsa-ed25519/sign | 127.0 µs |
| eddsa-ed25519/verify | 123.7 µs |
| rsa-pkcs-sha256/sign | 818.1 µs |
| rsa-pkcs-sha256/verify | 210.6 µs |
| rsa-pss-sha256/sign | 957.7 µs |
| rsa-pss-sha256/verify | 158.2 µs |